
Okay, so check this out—I’ve been noodling on custody for years. My gut kept nagging at the same problem: seed phrases are brilliant in theory, but messy in practice. Whoa! They become these fragile strings that everyone treats like ancient scripture. Initially I thought paper was the weak link, but then realized users’ behavior matters more; people lose slips, they mis-store words, and they rarely rehearse recovery under stress. Seriously? Yup. This part bugs me because we built crypto to be resilient, yet recovery often depends on human memory and luck.
Here’s the thing. Smart-card hardware wallets, the kind that look like a credit card but hold private keys securely, change the math. They feel familiar to most folks. Short sentence. Medium sentence that explains: they slot into phones or sit in a wallet and don’t demand you memorize a 24-word mantra. Longer thought that matters: when a device reduces cognitive load and aligns with daily habits—like paying or tapping a card—you actually see better security hygiene across the board, even among users who are not day traders or hardcore technologists.
My instinct said early on that removing the seed phrase would be risky. Hmm… but then I watched people adopt smart cards and the dynamic shifted. On one hand the seed phrase is portable and paper-resistant to electronics; though actually, on the other hand, smart cards centralize the key material in a tamper-evident chip so theft patterns change. Initially I worried about a single point of failure, but then realized redundancy strategies—like splitting backups across cards or using secure custodial options—fill that gap. I’m biased, but for non-custodial everyday use, the trade-offs are compelling.
Let me tell a quick story. I handed a smart-card wallet to a friend who is a total crypto novice. He tapped his phone, smiled, and asked where the recovery words were. He expected them. He was surprised when I said there weren’t any to memorize. He laughed. Really? He said. It was a revelation to him. He later kept the card in his wallet, and it sat there quietly for months. No paper scrap, no Post-it, no Google Drive file. That behavioral shift alone is huge—users who would otherwise write down seeds in insecure places suddenly have a cleaner path.
But the tech side matters, too. Short sentence. Hardware-backed key storage uses secure elements or smartcard chips that resist tampering. Medium sentence: these chips run secure firmware and often hold keys in a way that services can attest to without exposing secrets. Long sentence: the architecture allows operations such as signing transactions to occur inside the chip, meaning the private key never leaves the device, which reduces exposure to malware on phones or laptops while preserving interoperability with wallets and dApps when done correctly.
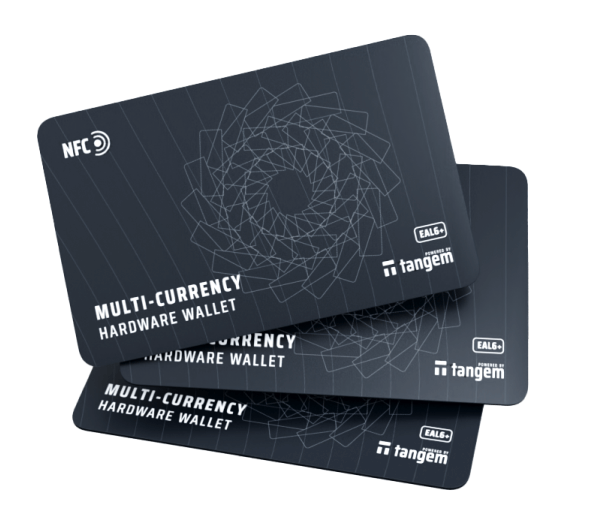
Real-world trade-offs and a practical pick: tangem hardware wallet
Look, no solution is flawless. Smart cards resolve many human problems but introduce others. Short sentence. For example, physical loss is still a risk and smart cards require reliable recovery schemes. Medium sentence: some companies offer a backup card pairing or a cloud-synced encrypted recovery, but that reintroduces centralized dependencies which many crypto-native users dislike. Longer thought: choosing a product is about what kind of risk you prefer—distributed paper backups that can be destroyed or forgotten, or a small physical token that fits in your wallet but might be stolen or damaged, and each path has mitigation strategies.
I’ll be honest—I like Tangem’s approach for several reasons. My first impression was “slick,” and that matters. But deeper down, Tangem builds smart cards that operate like contactless hardware wallets, they sign transactions securely, and they are designed to be dead-simple for mainstream users. Check this out—if you want a minimalist, resilient experience that removes 24-word recitation and instead uses a tap-and-sign model, the tangem hardware wallet is worth evaluating. I’m not saying it’s perfect; I’m saying it’s pragmatic for many people who prioritize ease without giving up the core security benefits of cold storage.
Now, let’s get tactical. Short sentence. If you try a smart-card wallet, test your recovery plan immediately. Medium sentence: buy two compatible cards and perform a full recovery from one using the other’s backup instructions, because the first time you need to restore should not be during a crisis. Long sentence: document the process in a secure way, consider geographically distributed backups (a card in a safe deposit box, another with a trusted person, or a sealed hardware pouch), and rehearse how you’d access funds if a phone dies or an account is locked, because real-world failure modes are usually unpredictable.
Something felt off about blind trust in any single vendor. So I dig into firmware update policies and open-source practices. Short sentence. Ask questions about attestation and whether the card supports third-party wallet connections. Medium sentence: ensure you can verify the device in-person and that recovery procedures don’t rely solely on a central server you don’t control. Long sentence: understand the supply chain too, because tampered devices at purchase time are a class of attack, and knowing where and how the card was manufactured, distributed, and sealed gives you real assurance beyond marketing copy.
On the user-experience front, smart cards shine. Short sentence. They remove barriers for onboarding friends and family. Medium sentence: instead of teaching someone to guard a list of words, you teach them to treat a plastic card like a credit card—keep it safe, don’t share it, know where backups are stored. Long sentence: for businesses managing payroll, NFTs, or community treasuries, the combination of NFC or secure signing can integrate seamlessly with workflows while preserving non-custodial control, which is a rare balance between user-friendliness and sovereignty.
Okay, so not all scenarios fit. High-value custodians might still want air-gapped multisig setups with hardware keycards spread across geographies, and very advanced users will prefer fully auditable open-source chains of custody. Short sentence. If you are running an exchange or institutional fund, the smart-card-only approach isn’t enough. Medium sentence: but for most retail users, hobbyists, or small teams, the smart-card model offers a massive improvement in actual security practices because it’s easier to do the right thing than to do the wrong thing. Long sentence: ease increases adoption, adoption reduces risky compromises like storing seeds in cloud notes, and that cumulative effect over thousands of users actually makes networks and ecosystems safer.
I’ll leave you with a couple of practical checks. Short sentence. First: verify how the device handles firmware updates and whether updates are signed. Medium sentence: second: check recovery design—does the system support multiple backup cards, or an air-gapped export, and are recovery steps documented in plain language? Longer sentence: third: test user flows with non-technical participants (a spouse, a parent), because if your less-technical contact can follow recovery steps without callouts or extra guidance, the product is doing something right and is likely to outperform a paper seed for day-to-day resilience.
Frequently asked questions
Do smart-card wallets eliminate the need for a seed phrase entirely?
Short answer: often yes, for user-facing recovery models. But there are nuances. Medium sentence: some smart-card systems use a backup card model, while others create encrypted recovery files or integrate multisig, so the practical result varies by vendor. Long sentence: evaluate the vendor’s recovery options carefully—elimination of a 24-word seed doesn’t mean removal of backup responsibility; it means the responsibility looks different and may be easier for many people.
What happens if the card is physically lost or damaged?
Short sentence. For many systems you can restore to a new card if you followed the vendor’s backup procedure. Medium sentence: that might mean using a paired backup card, an encrypted recovery code, or a split-recovery method, and each option has trade-offs between convenience and centralization. Long sentence: a practical approach is to plan for physical loss ahead of time: maintain at least one tested backup in a geographically separate secure location and rehearse recovery steps so that when a loss occurs you don’t have to improvise under stress.
Are smart cards safe against malware and remote attackers?
Short sentence. Yes—because signing occurs on the device, private keys don’t leave the chip. Medium sentence: this reduces exposure to malware on phones or computers that would otherwise intercept keys or tamper with transactions. Long sentence: however, phishing and social-engineering remain threats—attackers can craft malicious transaction requests or trick users into approving bad operations, so combine device security with careful transaction verification and user education.
